


Switched from SaaS Alerts
“From our standpoint, it's a big competitive advantage. It's autonomous, it's really quick, and it gives so much helpful information.”
Larry Brock
The AME Group
133
attacks stopped in 144 days
ConnectWise/SkyKick Incident Check is included in every Petra Scan through 11/13/26. Start yours here →


“Petra is a generation ahead of anybody else in M365 security.”
Petra's behavioral models analyze 30x more data than traditional location-first ITDRs, catching more real attacks with fewer false positives.
“I’ve done head-to-head comparisons — Petra was twice as fast. In a world where speed matters most, that’s the key differentiator.”
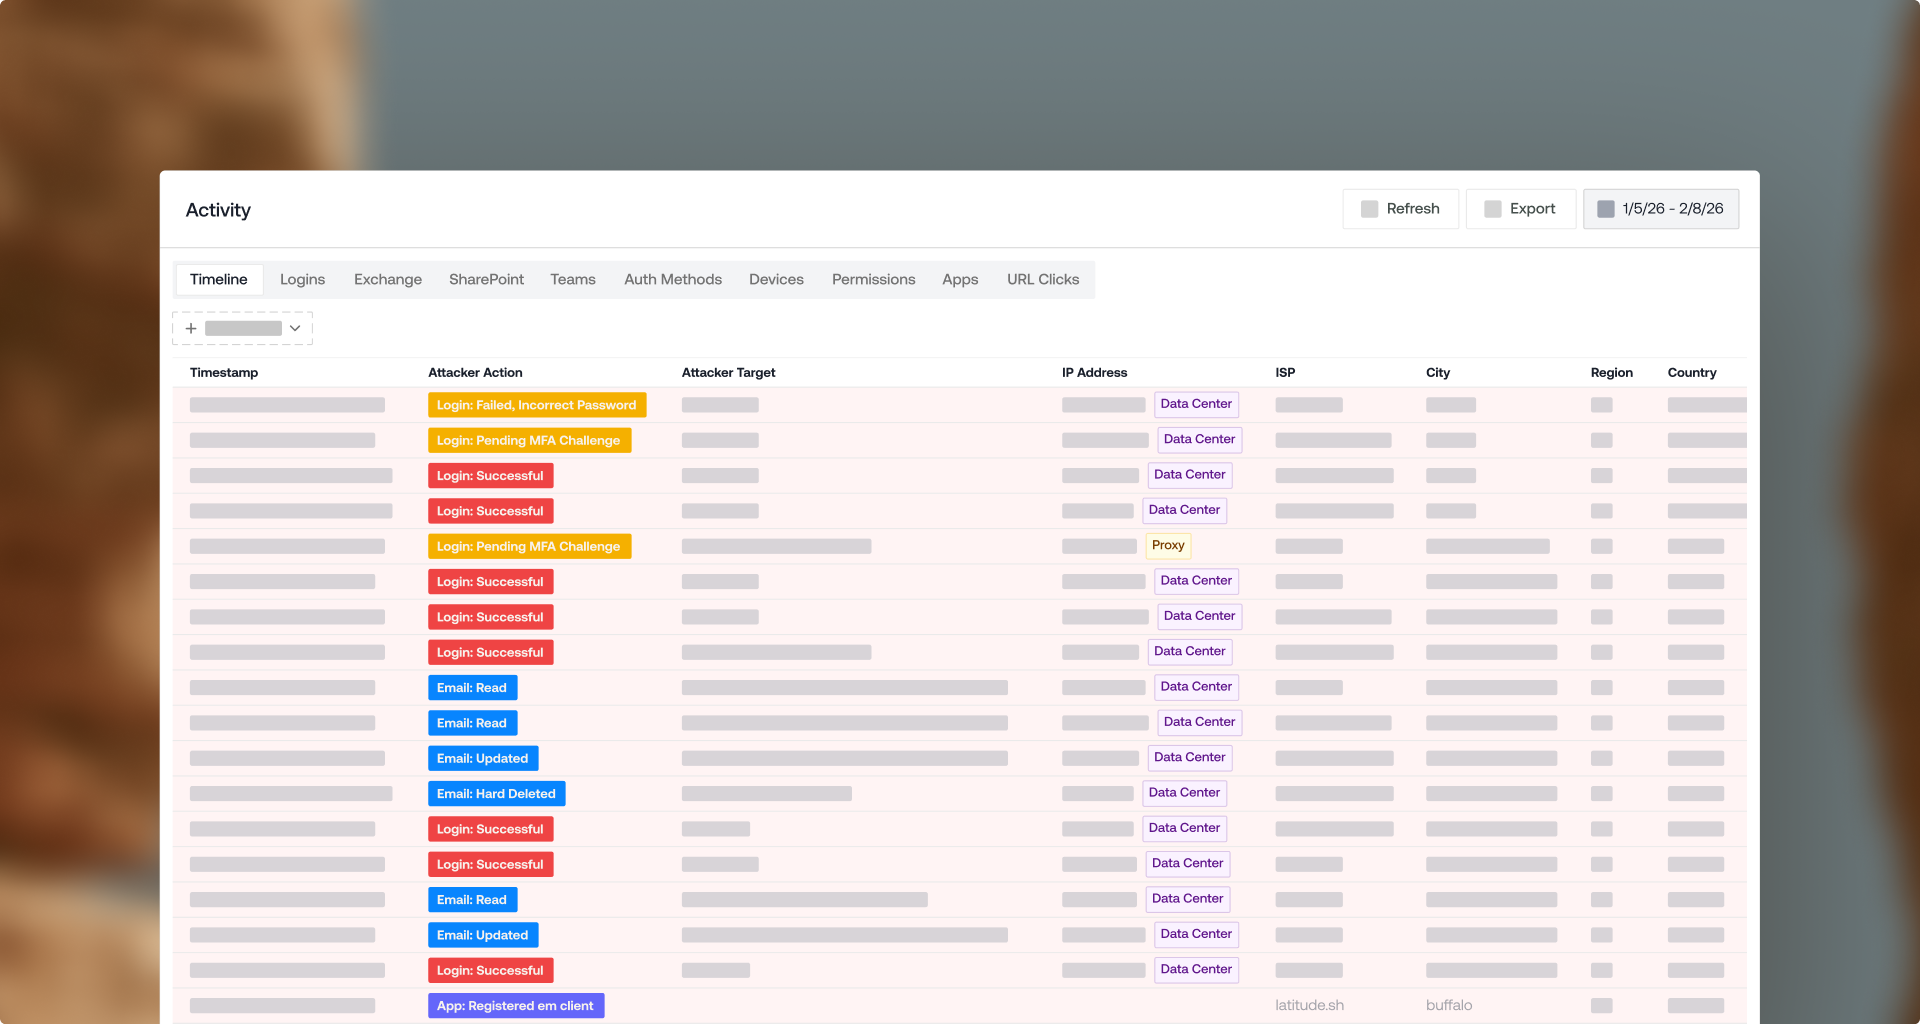
Our models parse the one thing attackers can't hide: their intent. With this approach, we catch what traditional location-based ITDRs miss, including residential proxies, valid sessions, and credentials that already passed MFA.
“Nobody's catching the stuff that Petra does, at the speed they do, with the clarity they give.”
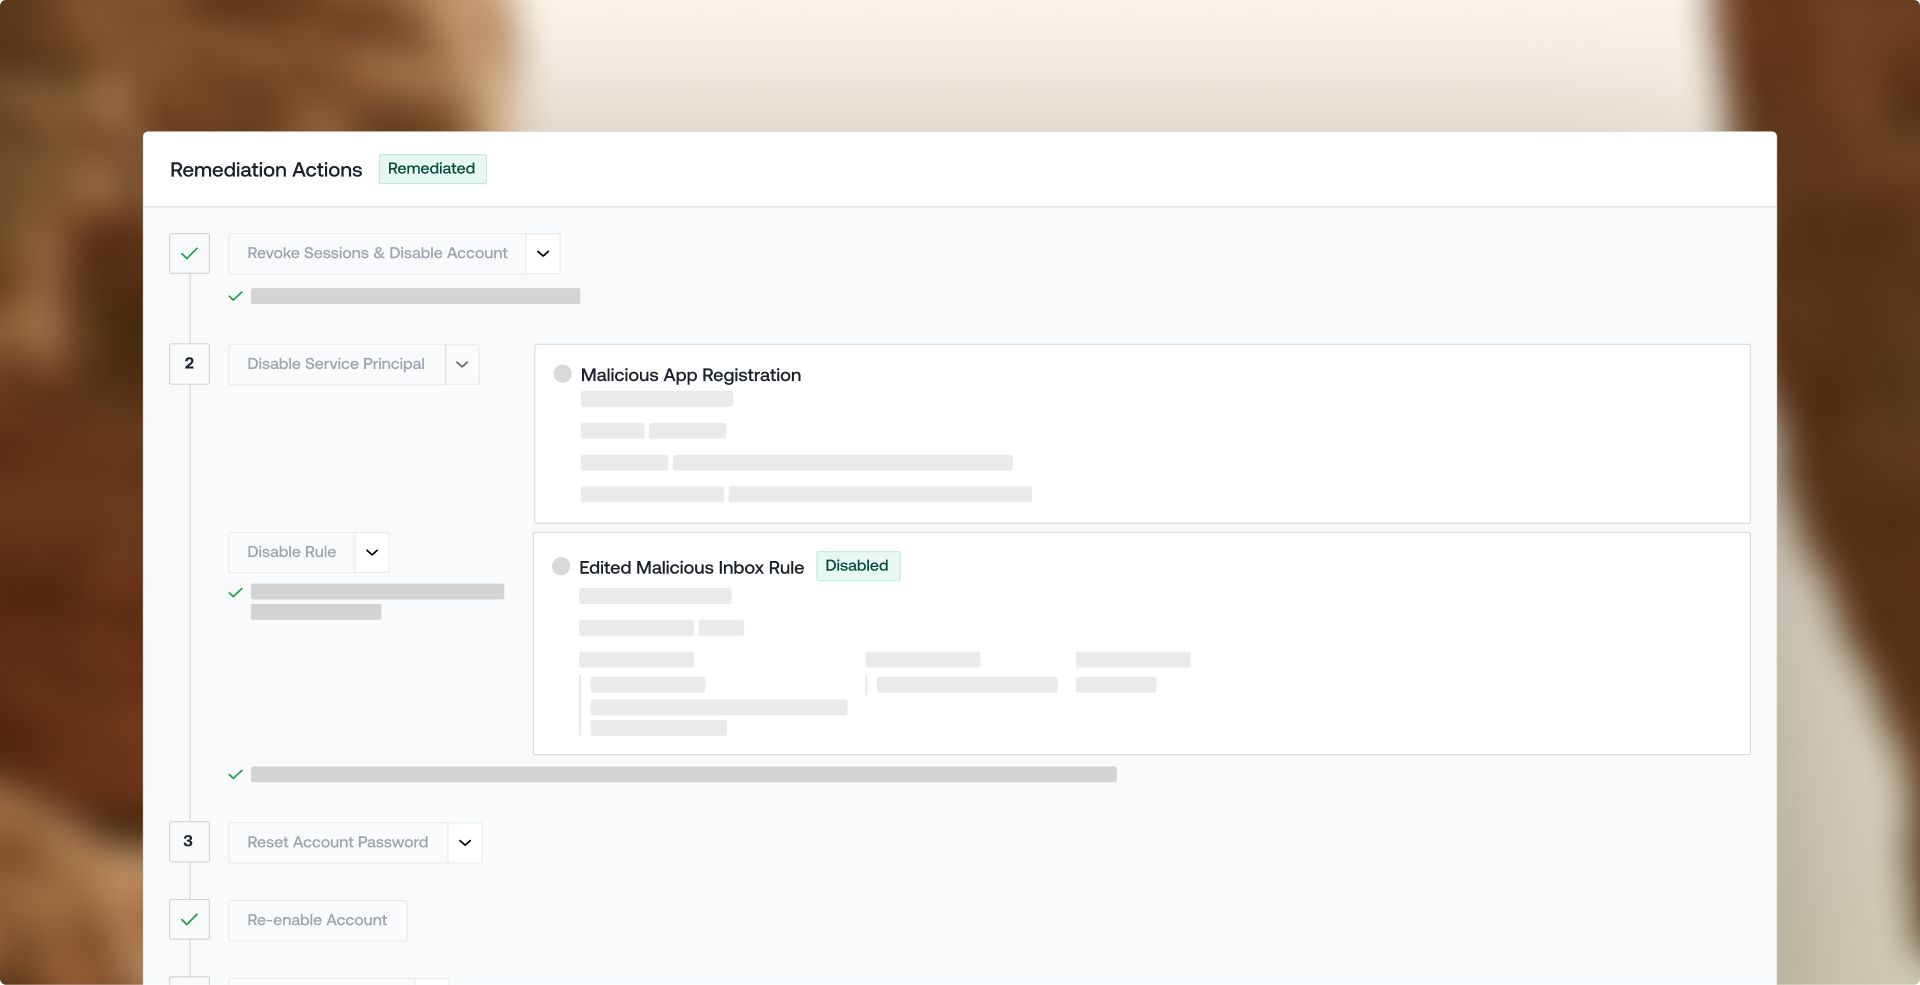
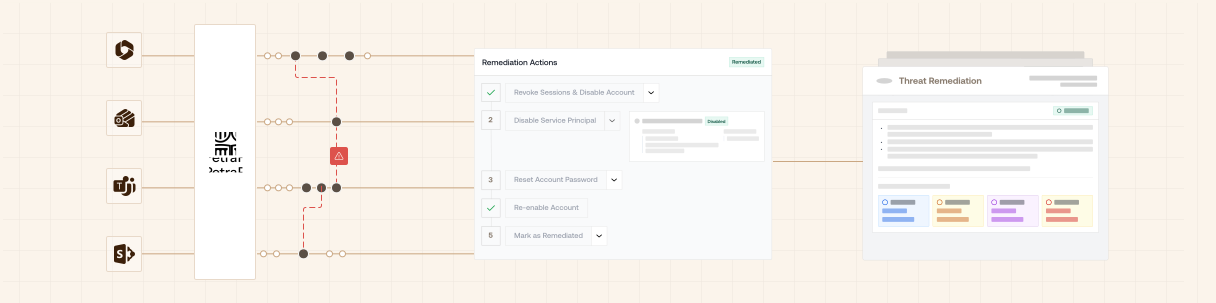
We remediate M365 compromises end-to-end, reversing every attacker action across sessions, devices, inbox rules, and registered applications.
“Before Petra, our team spent dozens of hours triaging alerts. Now, it's all just handled.”
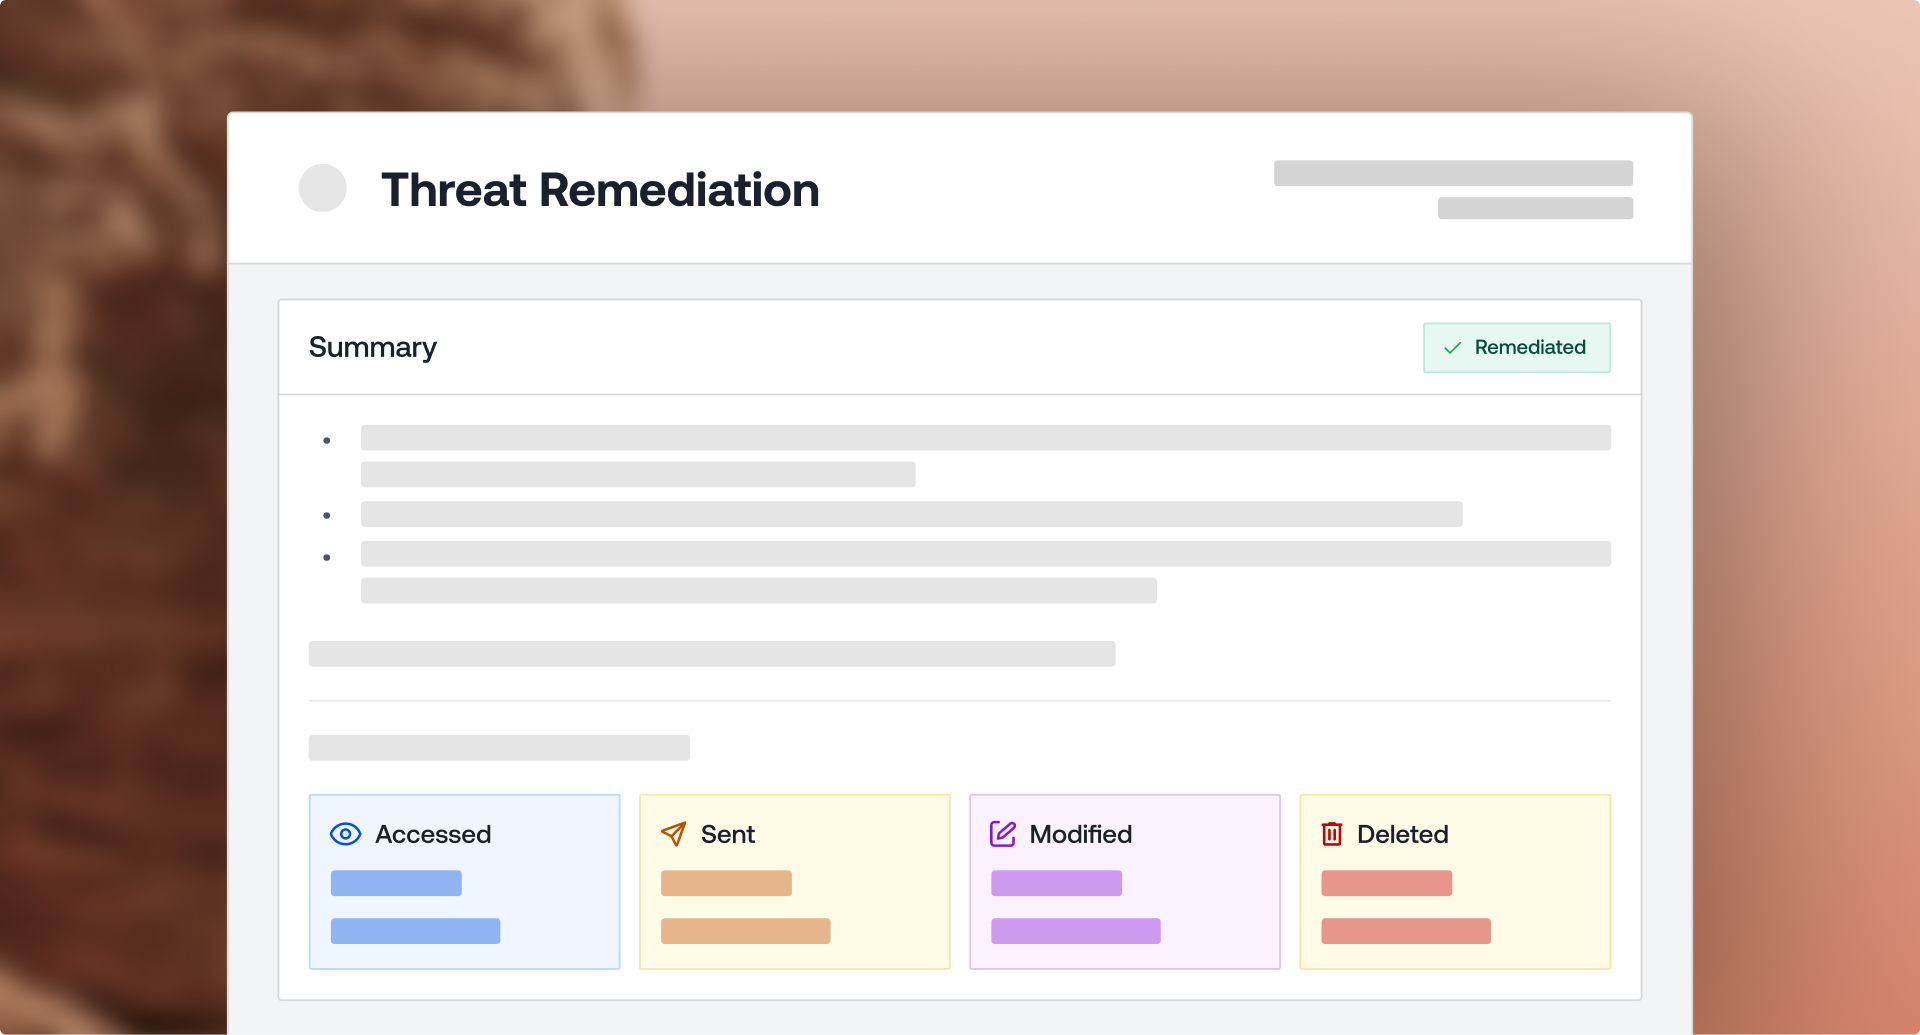
Every attack is documented with a full forensic timeline — what happened, when, and what was touched — so you have the full picture for clients, compliance, and insurance.
“Petra's reporting was visually stunning, simple for junior analysts, and clear for clients. It transformed client conversations from ‘Let me explain…’ to ‘Here’s how we protected you…’.”
Case studies
Hundreds of MSPs use Petra to protect their clients from identity attacks. Here's what they're seeing in the field.
Switched from SaaS Alerts
“From our standpoint, it's a big competitive advantage. It's autonomous, it's really quick, and it gives so much helpful information.”
Larry Brock
The AME Group
133
attacks stopped in 144 days
Switched from Huntress
“Not only did Petra catch 4 attacks that our prior ITDR whiffed on, it's also just really fast and intuitive for getting logs and reporting on incidents.”
Alex Appleton
Compu-SOLVE
4
residential proxy attacks caught in the first month
Business Growth
“It transformed client conversations from ‘Let me explain…’ to ‘Here's how we protected you…’. It's been a game-changer for us.”
Bill Hunt
AlignLayerNine
70%
reduction in false positives
Protect every client tenant from a single console, with multi-tenant deployment and reports.
Learn more
Add a differentiated ITDR to your catalog, with simple onboarding and co-branded materials.
Learn more
Reconstruct any BEC with root-cause forensics, a full attacker timeline, and client-ready reports.
Learn more
Secure your M365 environment with advanced behavioral detection and real-time remediation.
Learn moreGet insurance-grade forensics on the last 6 months of your M365 logs. Setup takes 5 minutes with results in 48 hours.